Free explainer · 8 pages · Sell and scale
SOC 2 shows your controls work. ISO 42001 shows how you run AI.
ISO 42001 or SOC 2: what enterprise buyers ask of your AI
Does our AI feature need ISO/IEC 42001, SOC 2, or both, and which comes first?
- For CTOs, VPs of Engineering and Heads of AI at U.S. B2B SaaS companies selling to enterprise
- Proposed approach · Explainer · 8 pages, PDF
What is inside
Know what SOC 2, ISO/IEC 27001 and ISO/IEC 42001 each tell a buyer, pick the one to pursue first from the asks you receive, and put the AI feature inside the SOC 2 scope you have.
- Harbor Ledger: five asks, one order of workA worked example
- Three answers to three questionsWhat each one covers
- Which first, by what your buyers askThe decision table
- Put the AI feature inside your SOC 2 scopeThe checklist
- Evidence first, claims secondFrom our work
- Bring this page to the Product ReviewYour notes for the call
This answers
What does each one cover, and what does neither show?
A SOC 2 report is a licensed CPA's examination of whether your controls work. ISO/IEC 27001 shows that security runs as one management system, and ISO/IEC 42001 shows that AI is governed with a policy, a risk list, owners and reviews. None of them shows whether your feature answers correctly for each customer; test runs and audit records show that.
Which should we pursue first, given what our buyers ask?
Count the asks in your last ten security reviews. If buyers ask for your SOC 2 report and then AI questions, put the AI feature inside SOC 2 scope first, and add ISO/IEC 42001 when buyers ask how you govern AI or name it in deals. If they ask AI questions without naming a standard, send evidence first: a test run, an audit record and an off switch.
What must the AI feature show inside our SOC 2 scope?
Name the model call, provider, region and every store a run writes to in the system description, and review the model provider like any other vendor. Limit who reaches prompts, models and retrieval, run prompt and model changes as reviewed and tested changes, and log every AI run with its user, customer, model version, output and approval.
You also get
- A worked example: five buyer asks and the order of work
- What SOC 2, ISO/IEC 27001 and ISO/IEC 42001 each tell a buyer
- A decision table by what your buyers ask, with what to send meanwhile
- A checklist to put the AI feature inside your SOC 2 scope
Free preview
Read the first 3 of 8 pages now
Free to read here, no form needed. The form opens the other 5 pages and the PDF.
Page 1 of 8Cover 
Page 2 of 8Harbor Ledger: five asks, one order of work 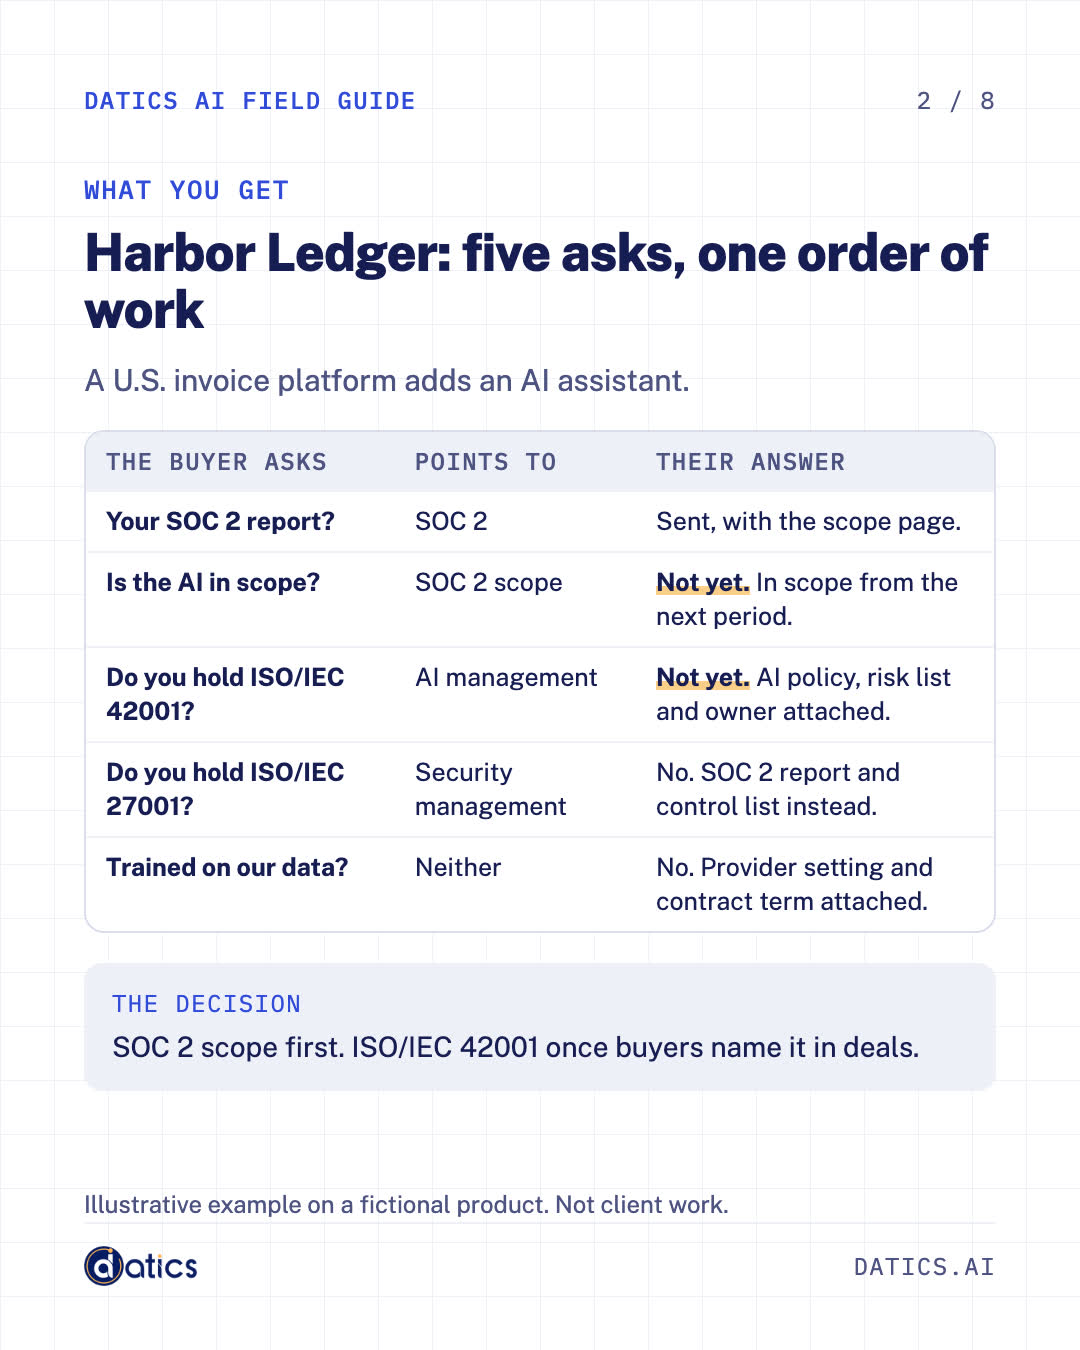
Page 3 of 8Three answers to three questions 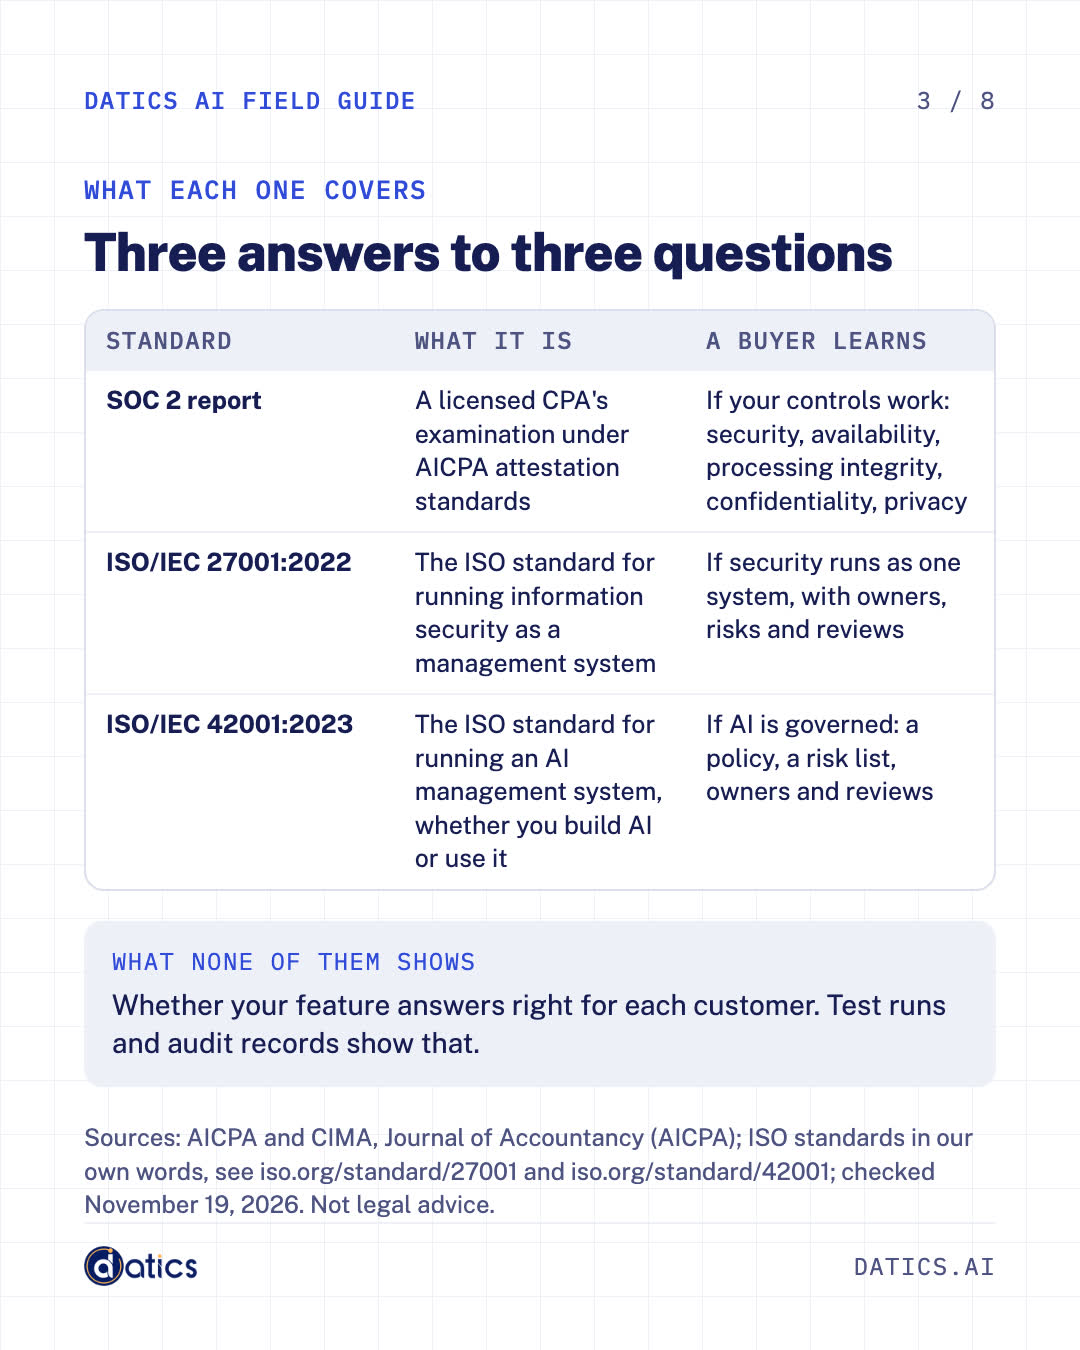
5 more pages after the form
The decision table, the SOC 2 scope checklist, proof from our work and a page to bring to the call.
- Page 4Which first, by what your buyers ask
- Page 5Put the AI feature inside your SOC 2 scope
- Page 6Evidence first, claims second
- Page 7Bring this page to the Product Review
- Page 8Find what your AI must show before the next review. Book a free 30-minute Product Review.
Related guides
More for the Sell and scale stage
Report · 15 pages
Start hereWhat will a customer's security team ask about our AI, and what do we attach?
Report: Getting your AI past a customer's security review
Get the reportTake the 5-minute checkReport · 15 pages
EdTechWhat do districts need to see about our AI before they sign?
Report: The district AI procurement pack
Get the reportReport · 15 pages
FintechIs this AI feature worth building, and can we price it without losing margin?
Report: Will this AI feature pay?
Get the reportTake the 4-minute check
Your customers already expect AI from your product.
Let us make it real inside the product you run today.