All guides
Free report
For product, engineering and IT leaders at U.S. software companies whose AI feature is waiting on a customer's security questionnaire
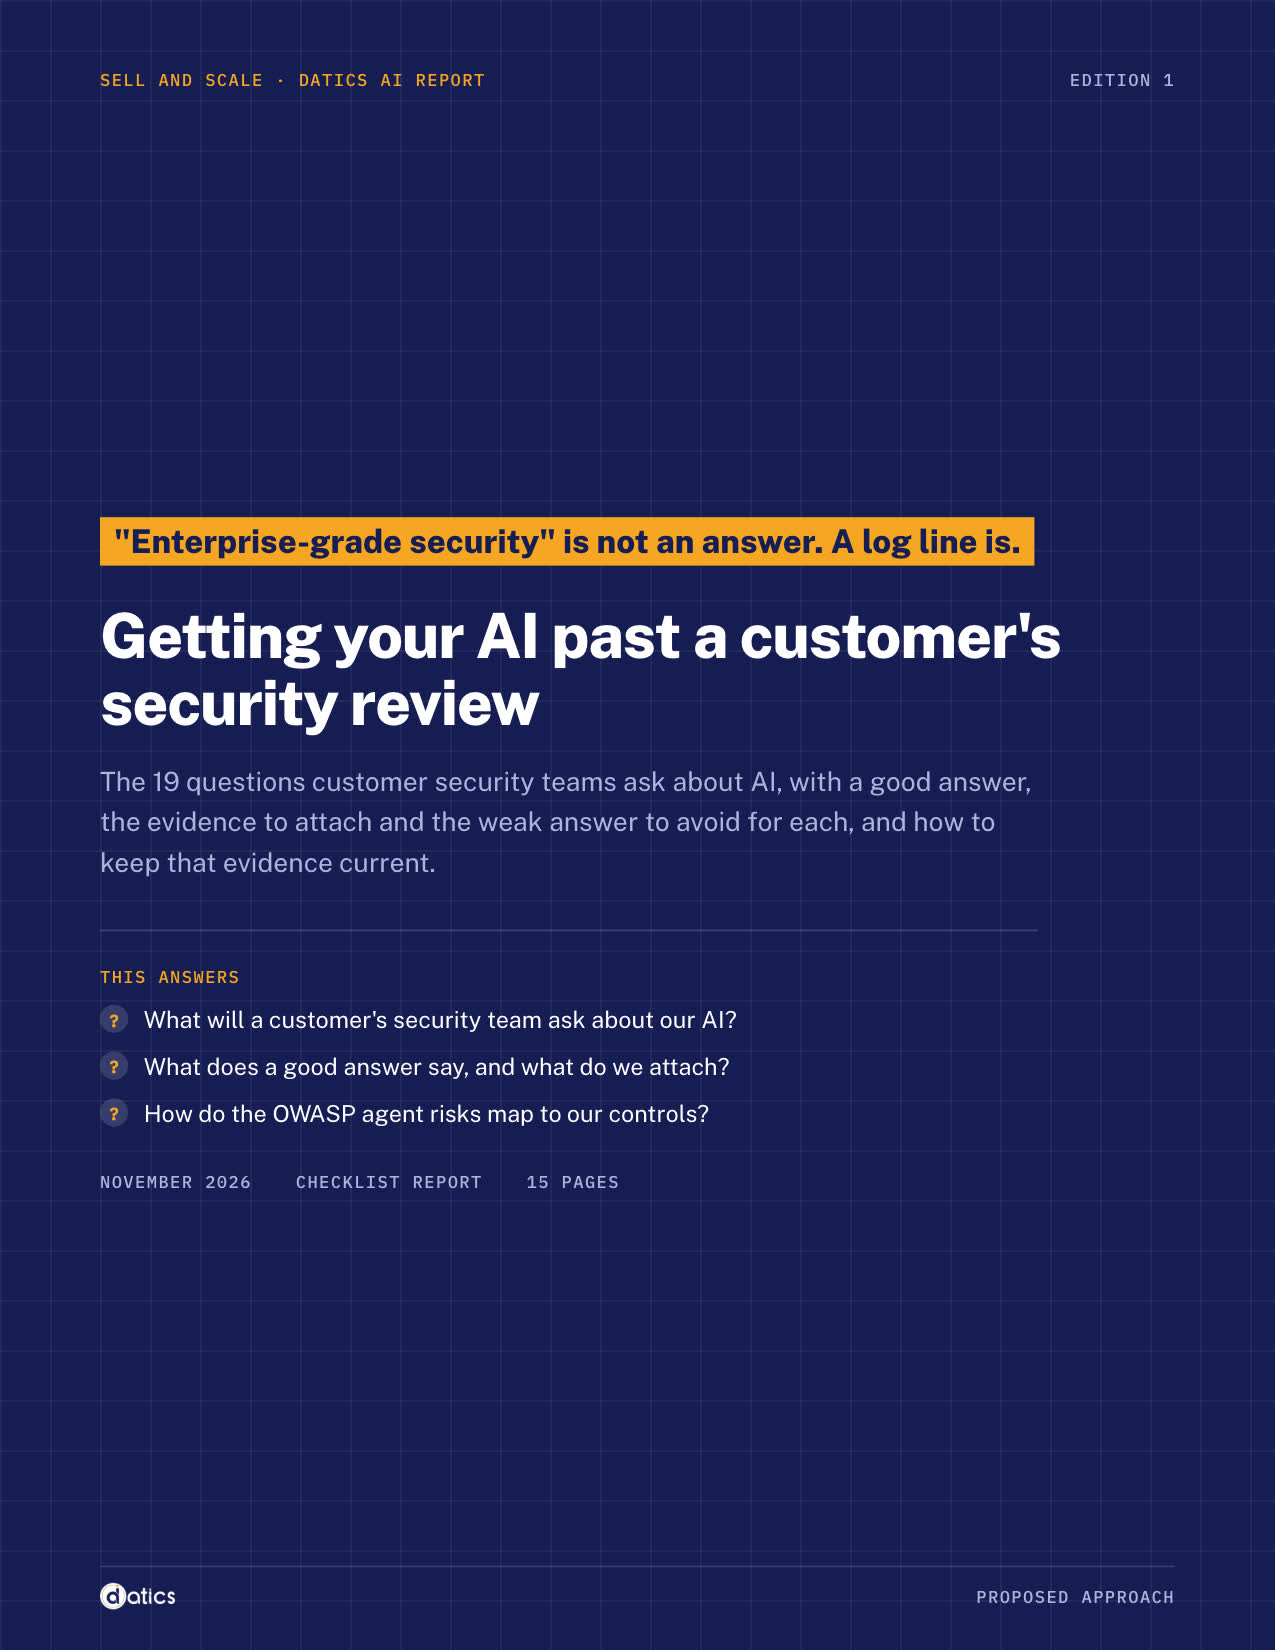
"Enterprise-grade security" is not an answer. A log line is.
Getting your AI past a customer's security review
The 19 questions customer security teams ask about AI, with a good answer, the evidence to attach and the weak answer to avoid for each, and how to keep that evidence current.
This answers
- What will a customer's security team ask about our AI?
- What does a good answer say, and what do we attach?
- How do the OWASP agent risks map to our controls?
Report · 15 pages, PDF · Proposed approach
Take the 5-minute check Answer a few questions and see your own result first.
What is inside
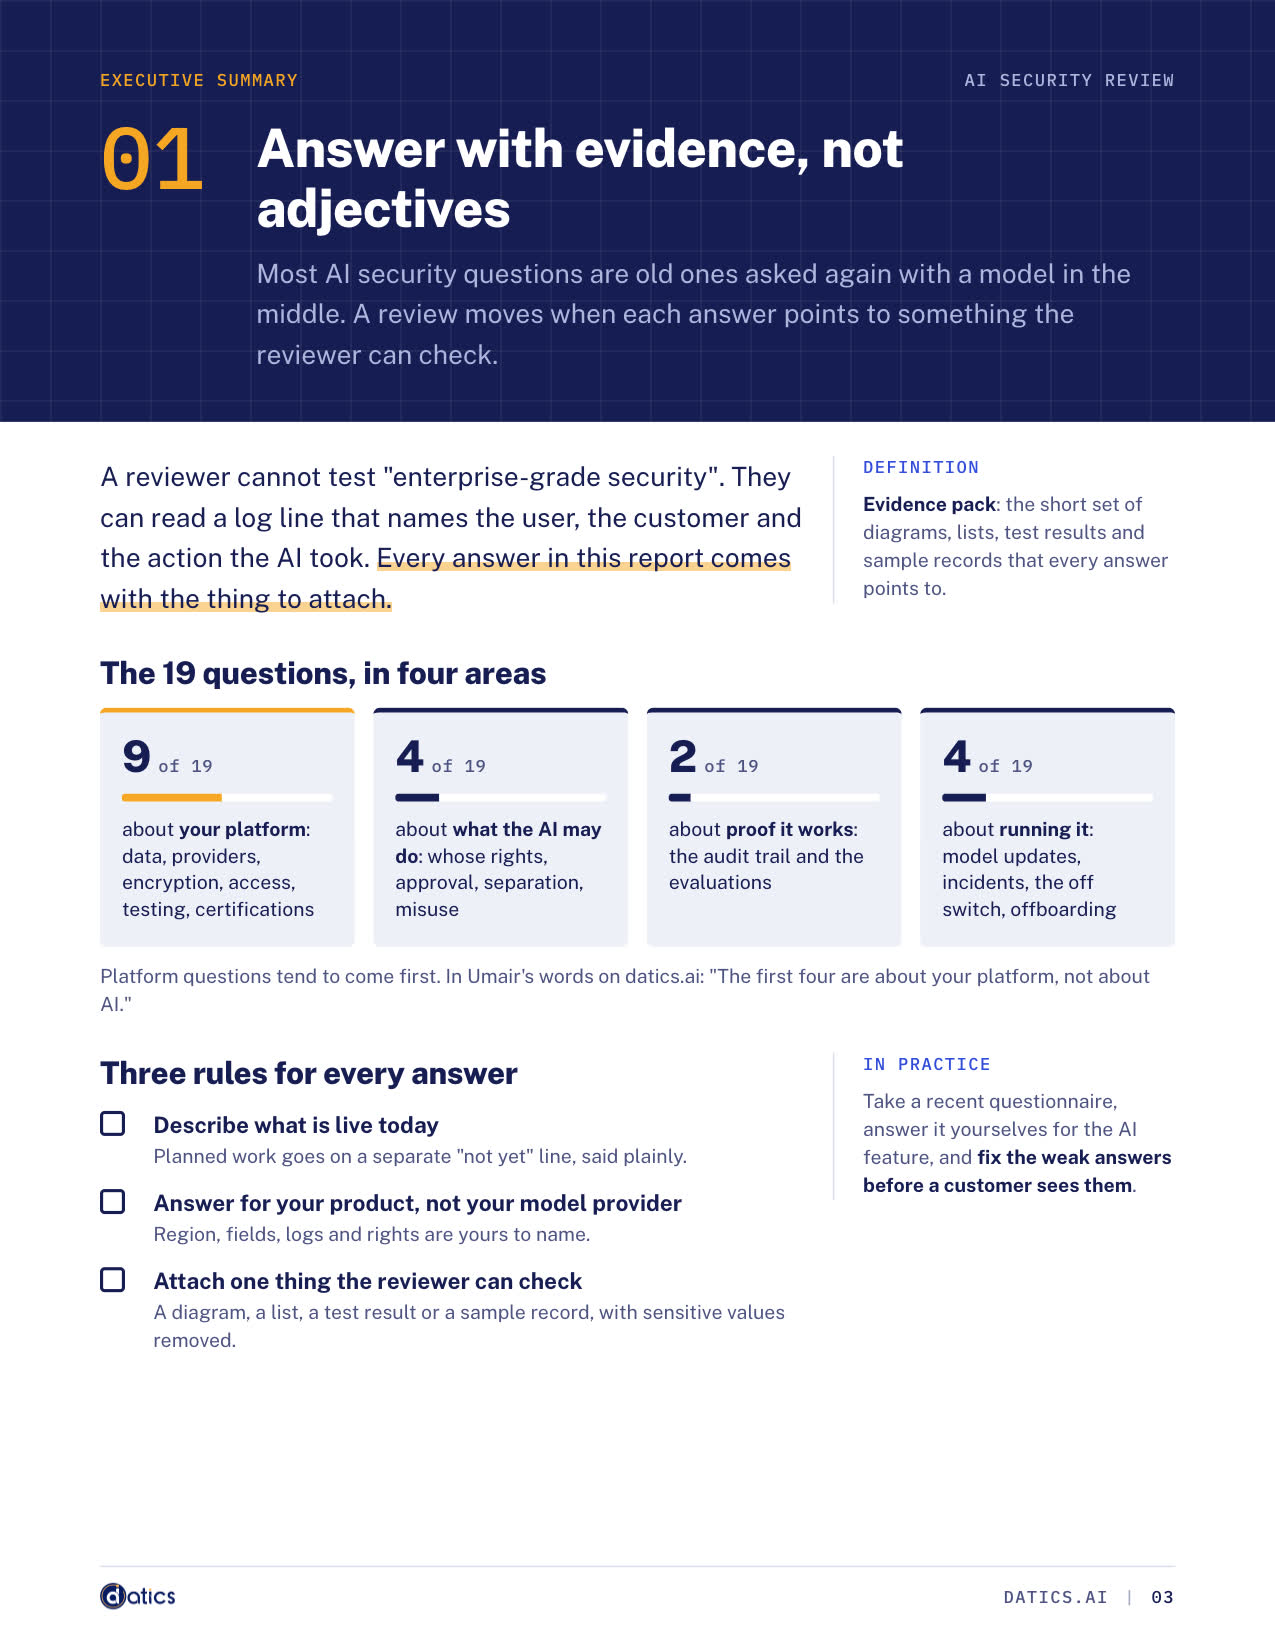
- 1Answer with evidence, not adjectivesExecutive summary
- 2Your platform comes firstYour platform
- 3What the AI may doWhat the AI may do
- 4Prove it, and run it safelyProof and operations
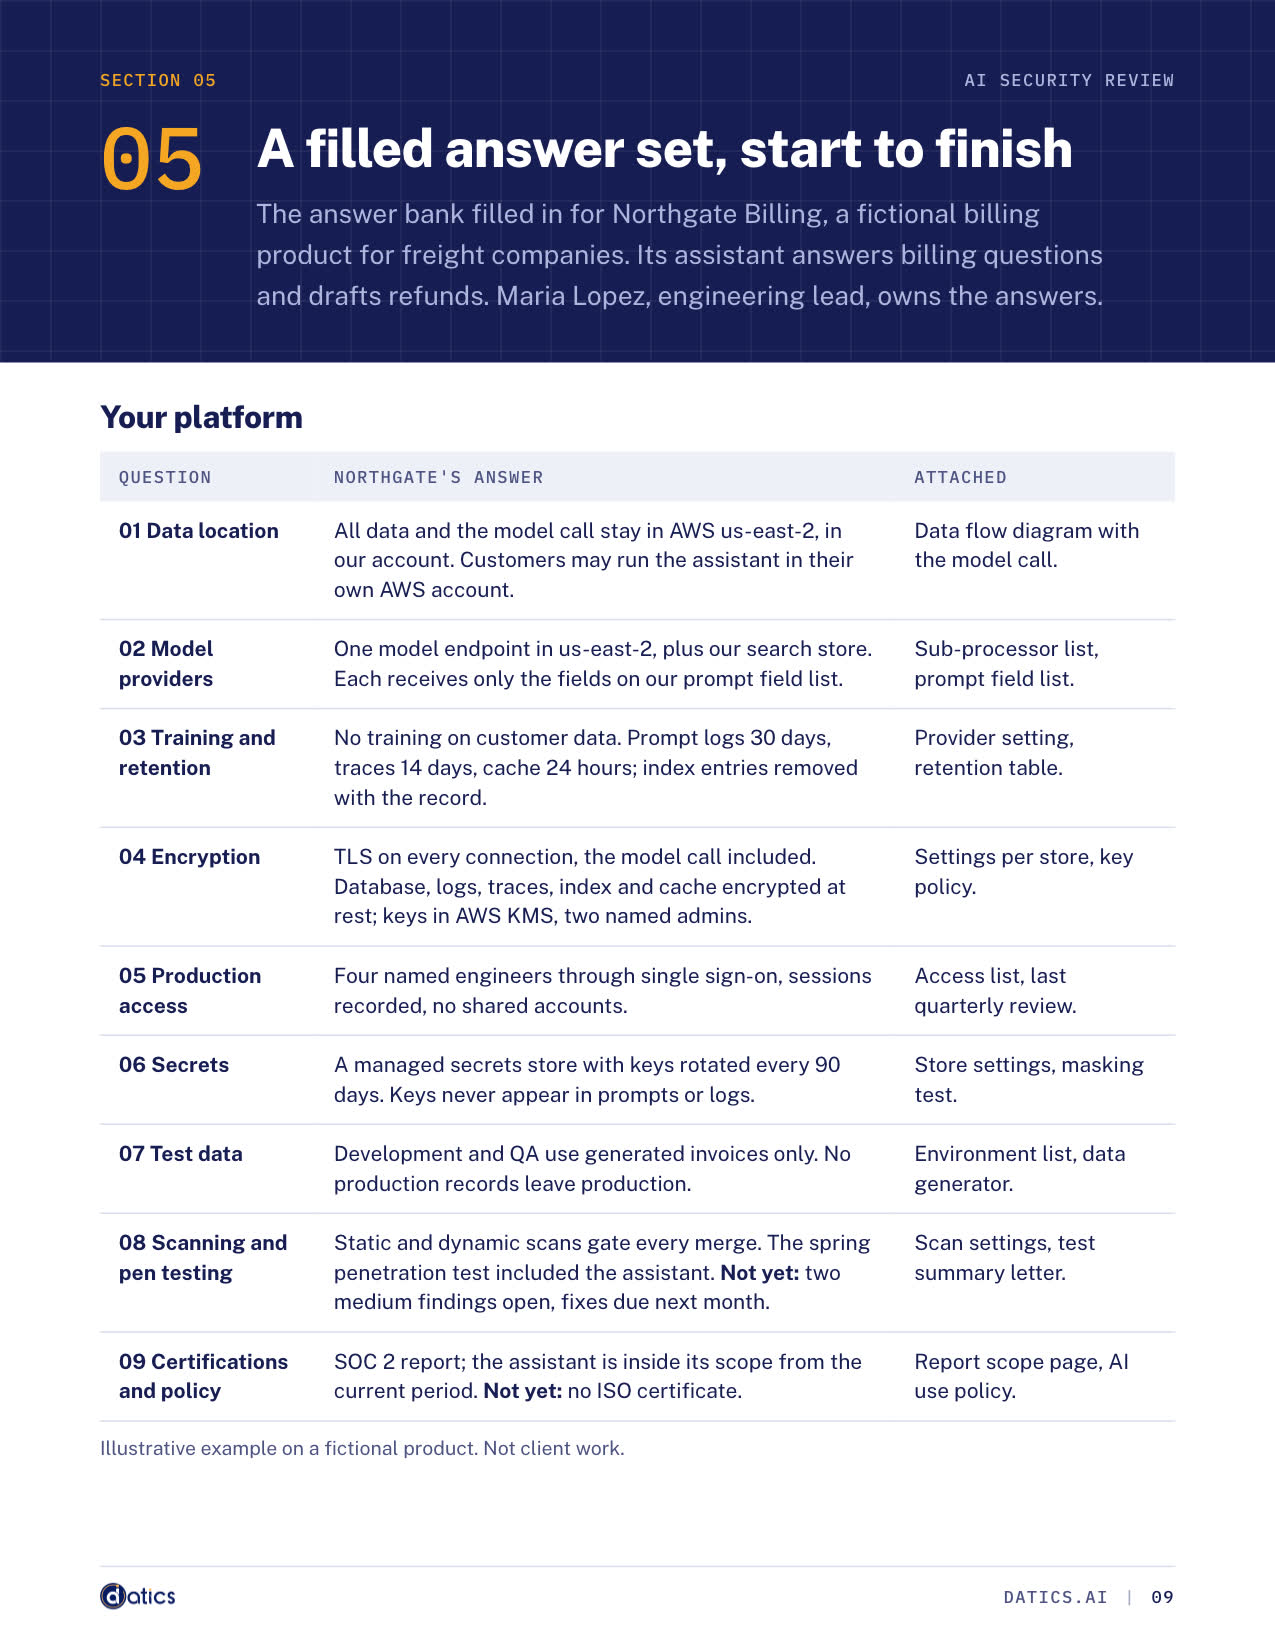
- 5A filled answer set, start to finishWorked example
- 6OWASP's ten agent risks, mapped to controlsOWASP agent risks
- 7Build the evidence pack once, keep it currentThe evidence pack
- 8Bring this page to the Product ReviewYour results
You also get
- The 19 questions customer security teams ask about AI, from data location to whose rights the AI uses
- A good answer, the evidence to attach and the weak answer to avoid, for every question
- A filled answer set for a fictional product
- OWASP's ten agent risks, each mapped to a control
- The questionnaire formats buyers send (SIG, CAIQ, HECVAT), and how to keep the evidence pack current
Preview